Allan Brothers Fruit
auroraThis record tracks a ransomware attack claimed by the aurora group against Allan Brothers Fruit. It collects the publicly disclosed attack details — sector, location and timeline — as published on the operator's leak site and indexed by Dark Eye.
Window Zero
EXPOSURE GAPWindow Zero is the time the breach stayed in the open before anyone said so — the gap between when the attack was first discovered on the operator's leak site (t1) and when it was publicly disclosed (t2). The wider this window, the longer victims, staff and customers were exposed with no warning.
Attack Summary
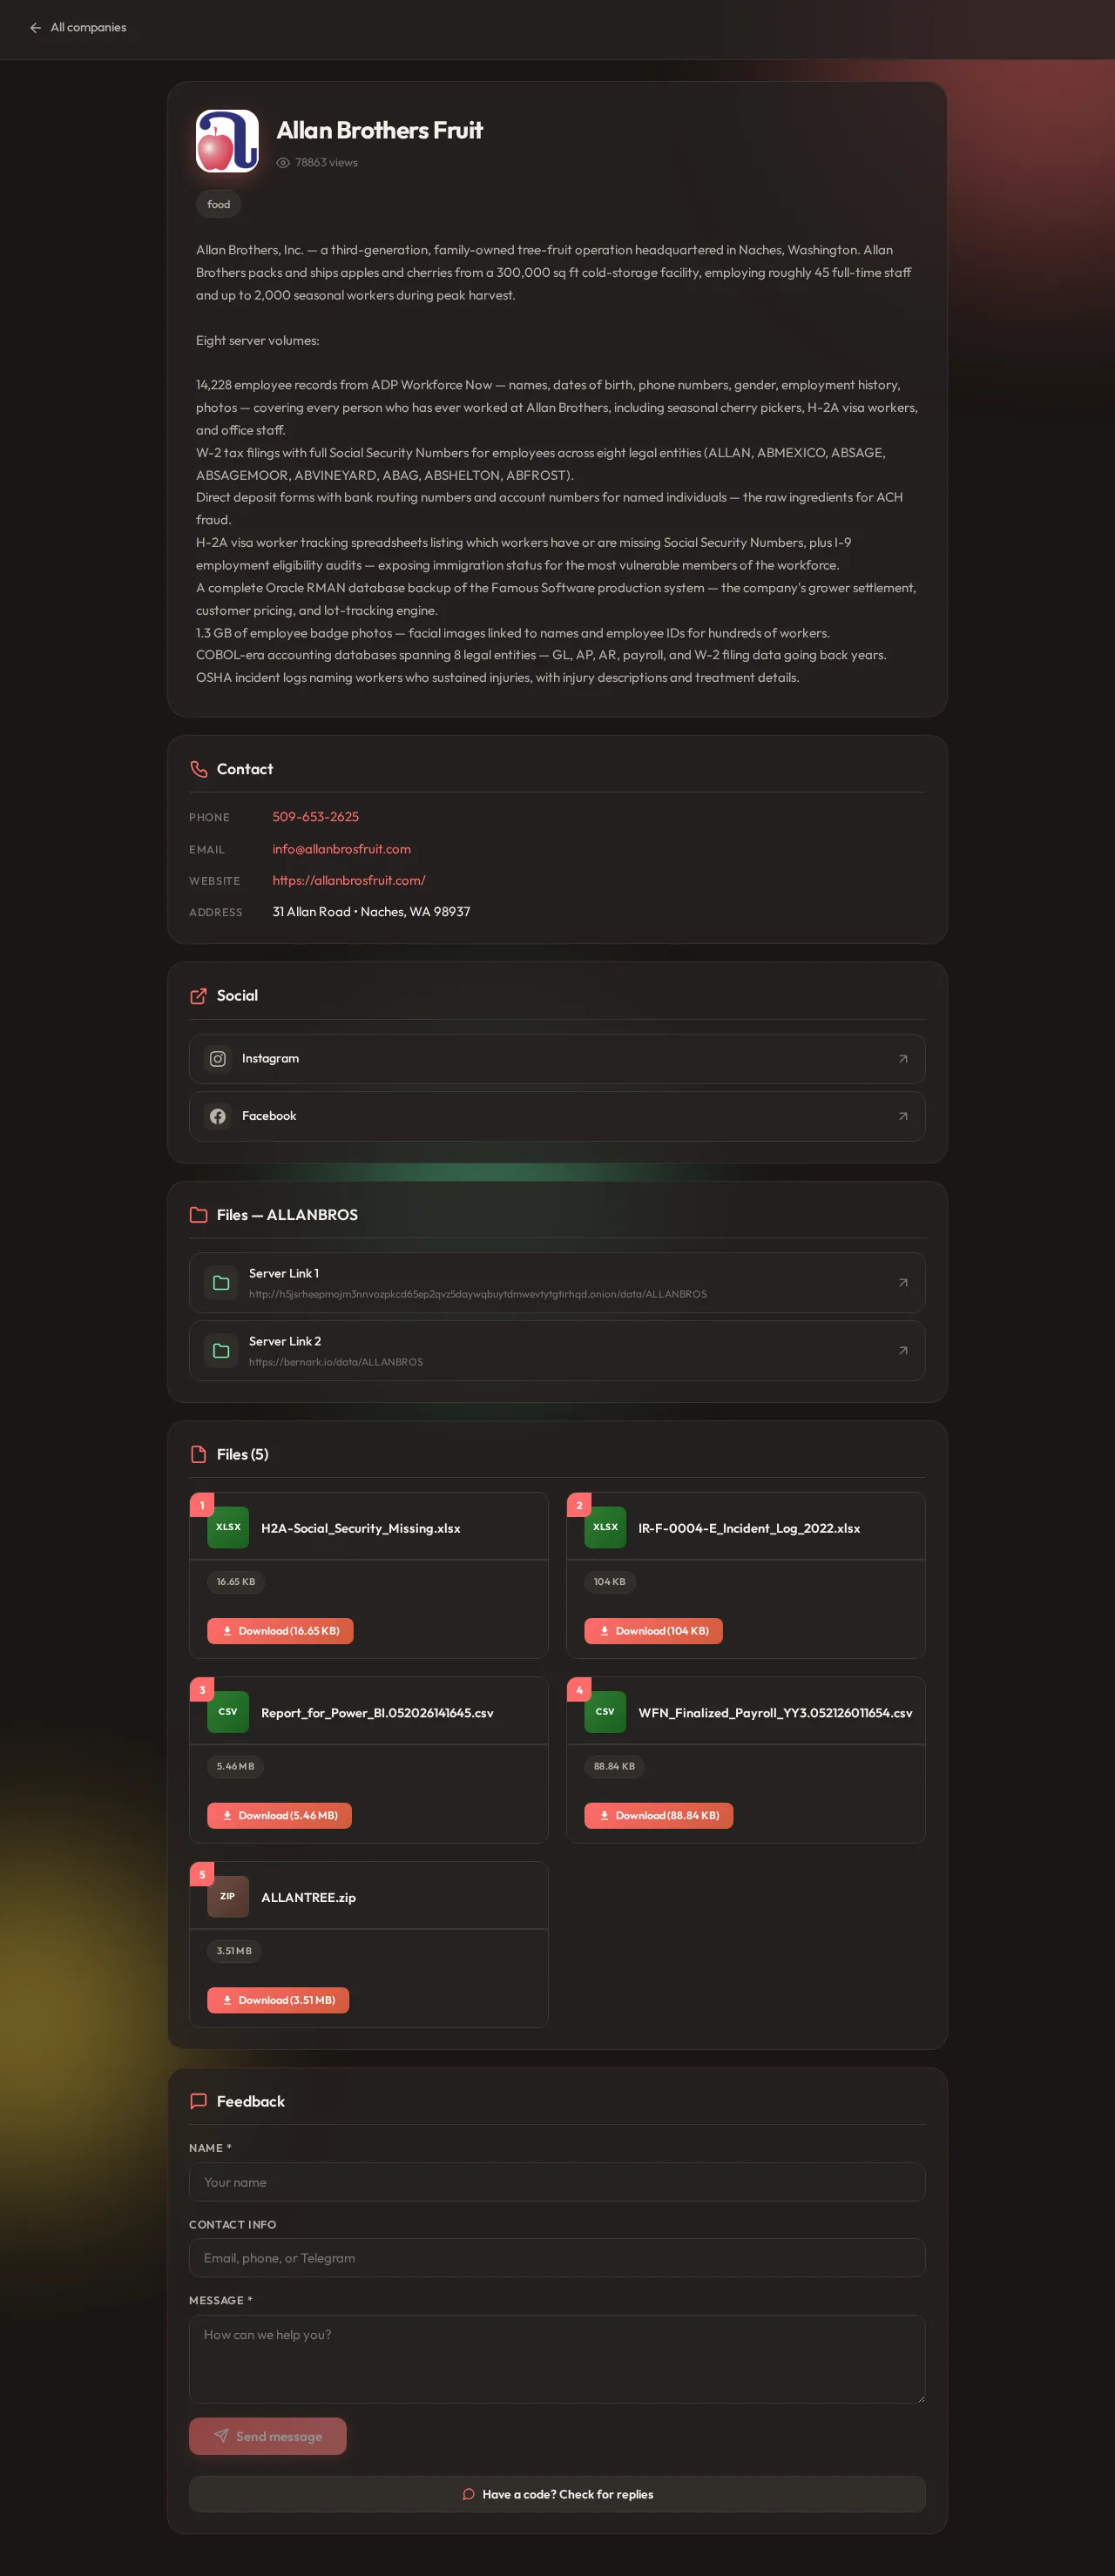
[food] Allan Brothers, Inc. — a third-generation, family-owned tree-fruit operation headquartered in Naches, Washington. Allan Brothers packs and ships apples and cherries from a 300,000 sq ft cold-storage facility, employing roughly 45 full-time staff and up to 2,000 seasonal workers during peak harvest. Eight server volumes: 14,228 employee records from ADP Workforce Now — names, dates of birth, phone numbers, gender, employment history, photos — covering every person who has ever worked at Allan Brothers, including seasonal cherry pickers, H-2A visa workers, and office staff. W-2 tax filings with full Social Security Numbers for employees across eight legal entities (ALLAN, ABMEXICO, ABSAGE, ABSAGEMOOR, ABVINEYARD, ABAG, ABSHELTON, ABFROST). Direct deposit forms with bank routing numbers and account numbers for named individuals — the raw ingredients for ACH fraud. H-2A visa worker tracking spreadsheets listing which workers have or are missing Social Security Numbers, plus I-9 employment eligibility audits — exposing immigration status for the most vulnerable members of the workforce. A complete Oracle RMAN database backup of the Famous Software production system — the company's grower settlement, customer pricing, and lot-tracking engine. 1.3 GB of employee badge photos — facial images linked to names and employee IDs for hundreds of workers. COBOL-era accounting databases spanning 8 legal entities — GL, AP, AR, payroll, and W-2 filing data going back years. OSHA incident logs naming workers who sustained injuries, with injury descriptions and treatment details.
Leak Screenshots
1 CAPTUREDCaptured directly from the operator's leak site by our collector, last checked 2026-09-01. Verdict evidence: [M1] Files (5) with multiple downloadable files listed, including XLSX, CSV, and ZIP files.
Capture history — 4 day(s) tracked. Content is locked.