Chip 1 Exchange
auroraThis record tracks a ransomware attack claimed by the aurora group against Chip 1 Exchange. It collects the publicly disclosed attack details — sector, location and timeline — as published on the operator's leak site and indexed by Dark Eye.
Window Zero
EXPOSURE GAPWindow Zero is the time the breach stayed in the open before anyone said so — the gap between when the attack was first discovered on the operator's leak site (t1) and when it was publicly disclosed (t2). The wider this window, the longer victims, staff and customers were exposed with no warning.
Attack Summary
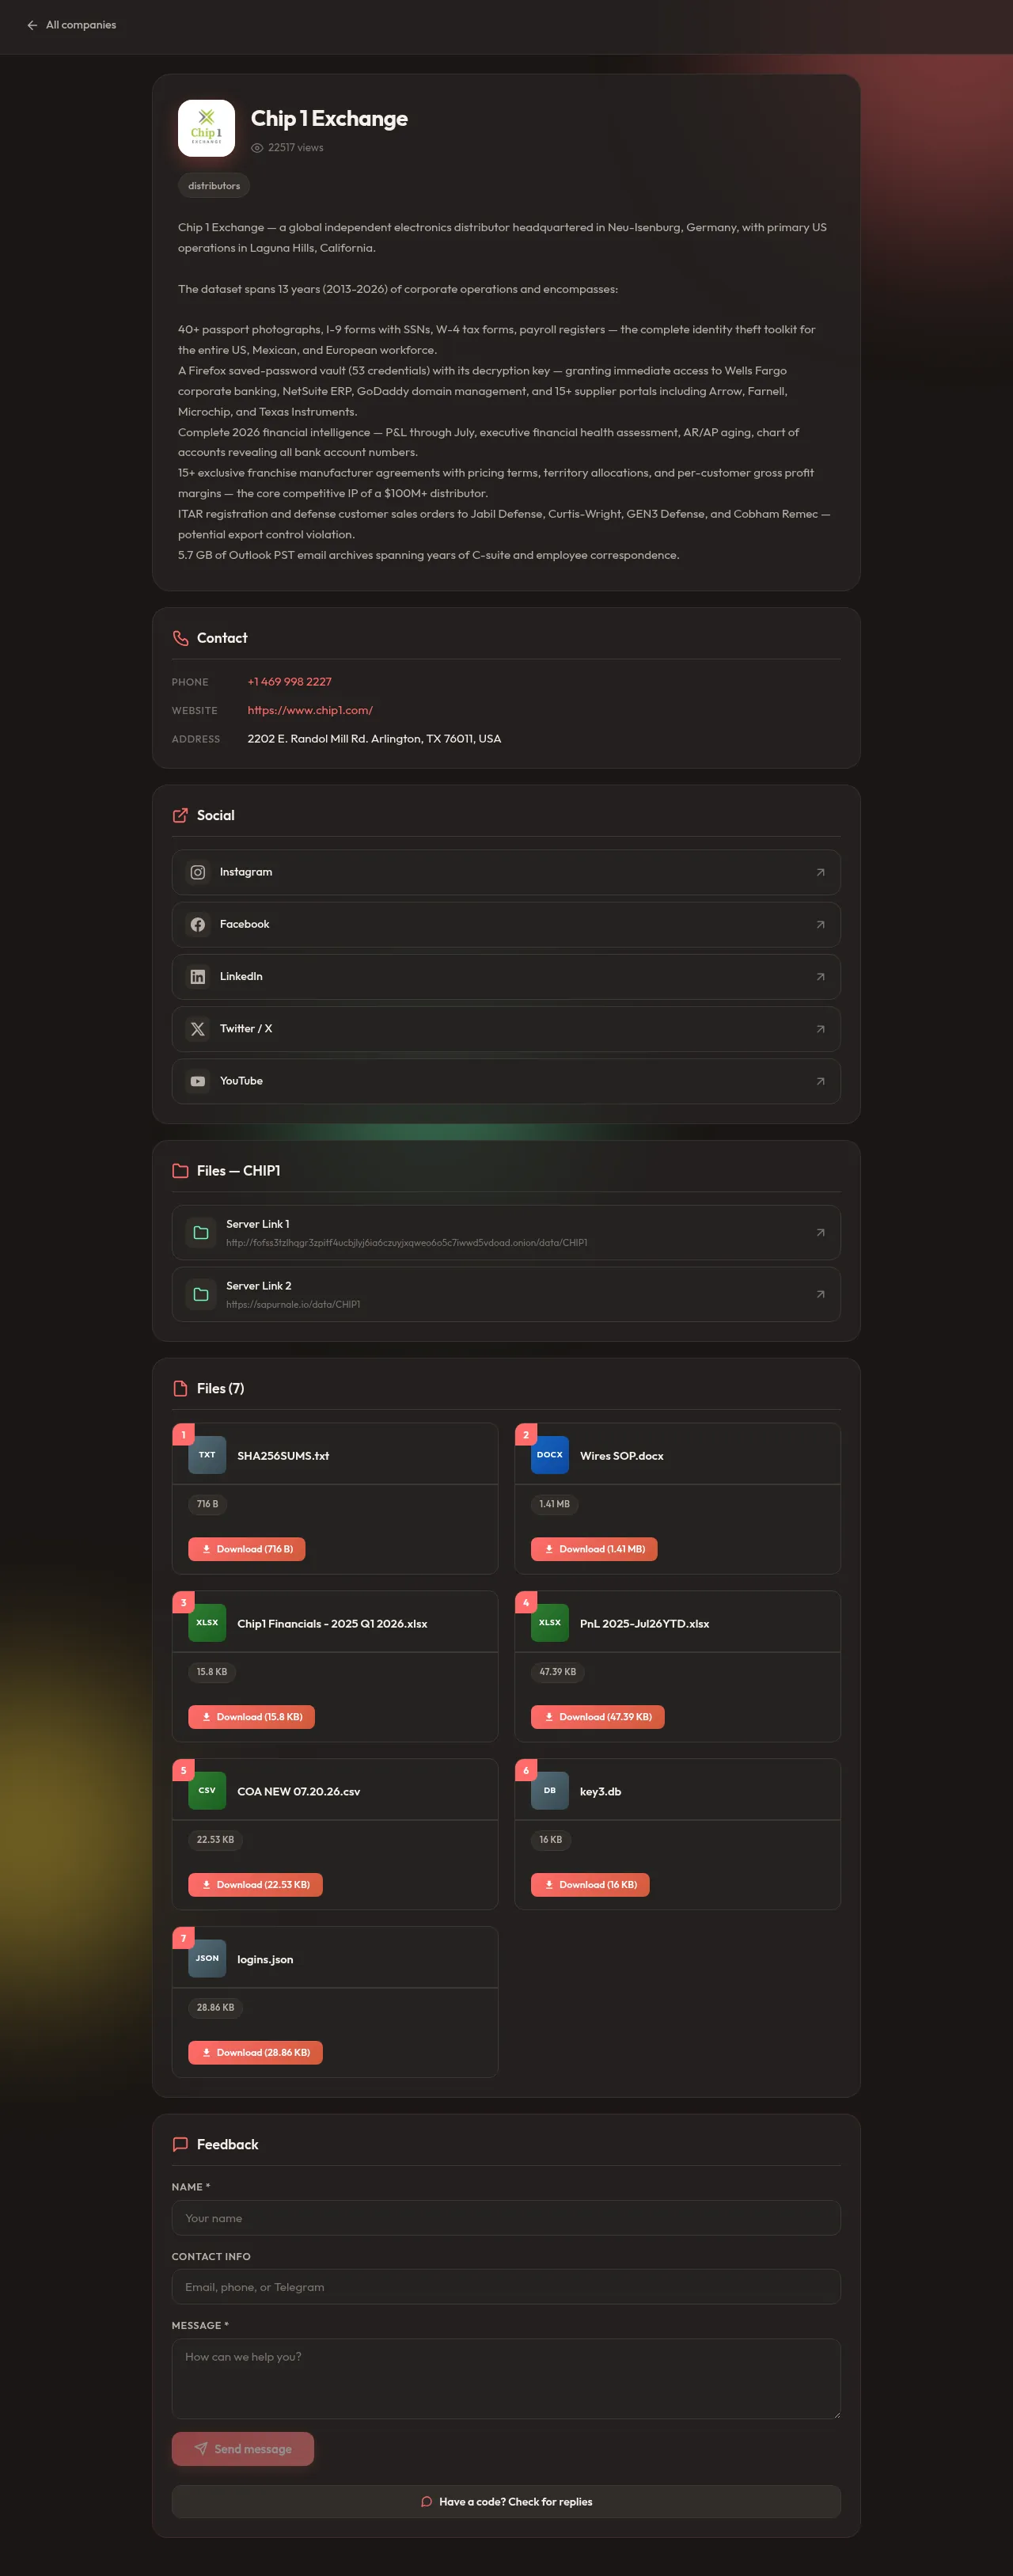
[distributor] Chip 1 Exchange — a global independent electronics distributor headquartered in Neu-Isenburg, Germany, with primary US operations in Laguna Hills, California. The dataset spans 13 years (2013-2026) of corporate operations and encompasses: 40+ passport photographs, I-9 forms with SSNs, W-4 tax forms, payroll registers. <redacted> Complete 2026 financial intelligence — P&L through July, executive financial health assessment, AR/AP aging, chart of accounts revealing all bank account numbers. 15+ exclusive franchise manufacturer agreements with pricing terms, territory allocations, and per-customer gross profit margins. ITAR registration and defense customer sales orders to Jabil Defense, Curtis-Wright, GEN3 Defense, and Cobham Remec. 5.7 GB of Outlook PST email archives spanning years of C-suite and employee correspondence.
Leak Screenshots
1 CAPTUREDCaptured directly from the operator's leak site by our collector, last checked 2026-10-02. Verdict evidence: [A1] Own Files section provides published server links
Capture history — 3 day(s) tracked. Content is locked.