Diamond Truck Centres
auroraThis record tracks a ransomware attack claimed by the aurora group against Diamond Truck Centres. It collects the publicly disclosed attack details — sector, location and timeline — as published on the operator's leak site and indexed by Dark Eye.
Window Zero
EXPOSURE GAPWindow Zero is the time the breach stayed in the open before anyone said so — the gap between when the attack was first discovered on the operator's leak site (t1) and when it was publicly disclosed (t2). The wider this window, the longer victims, staff and customers were exposed with no warning.
Attack Summary
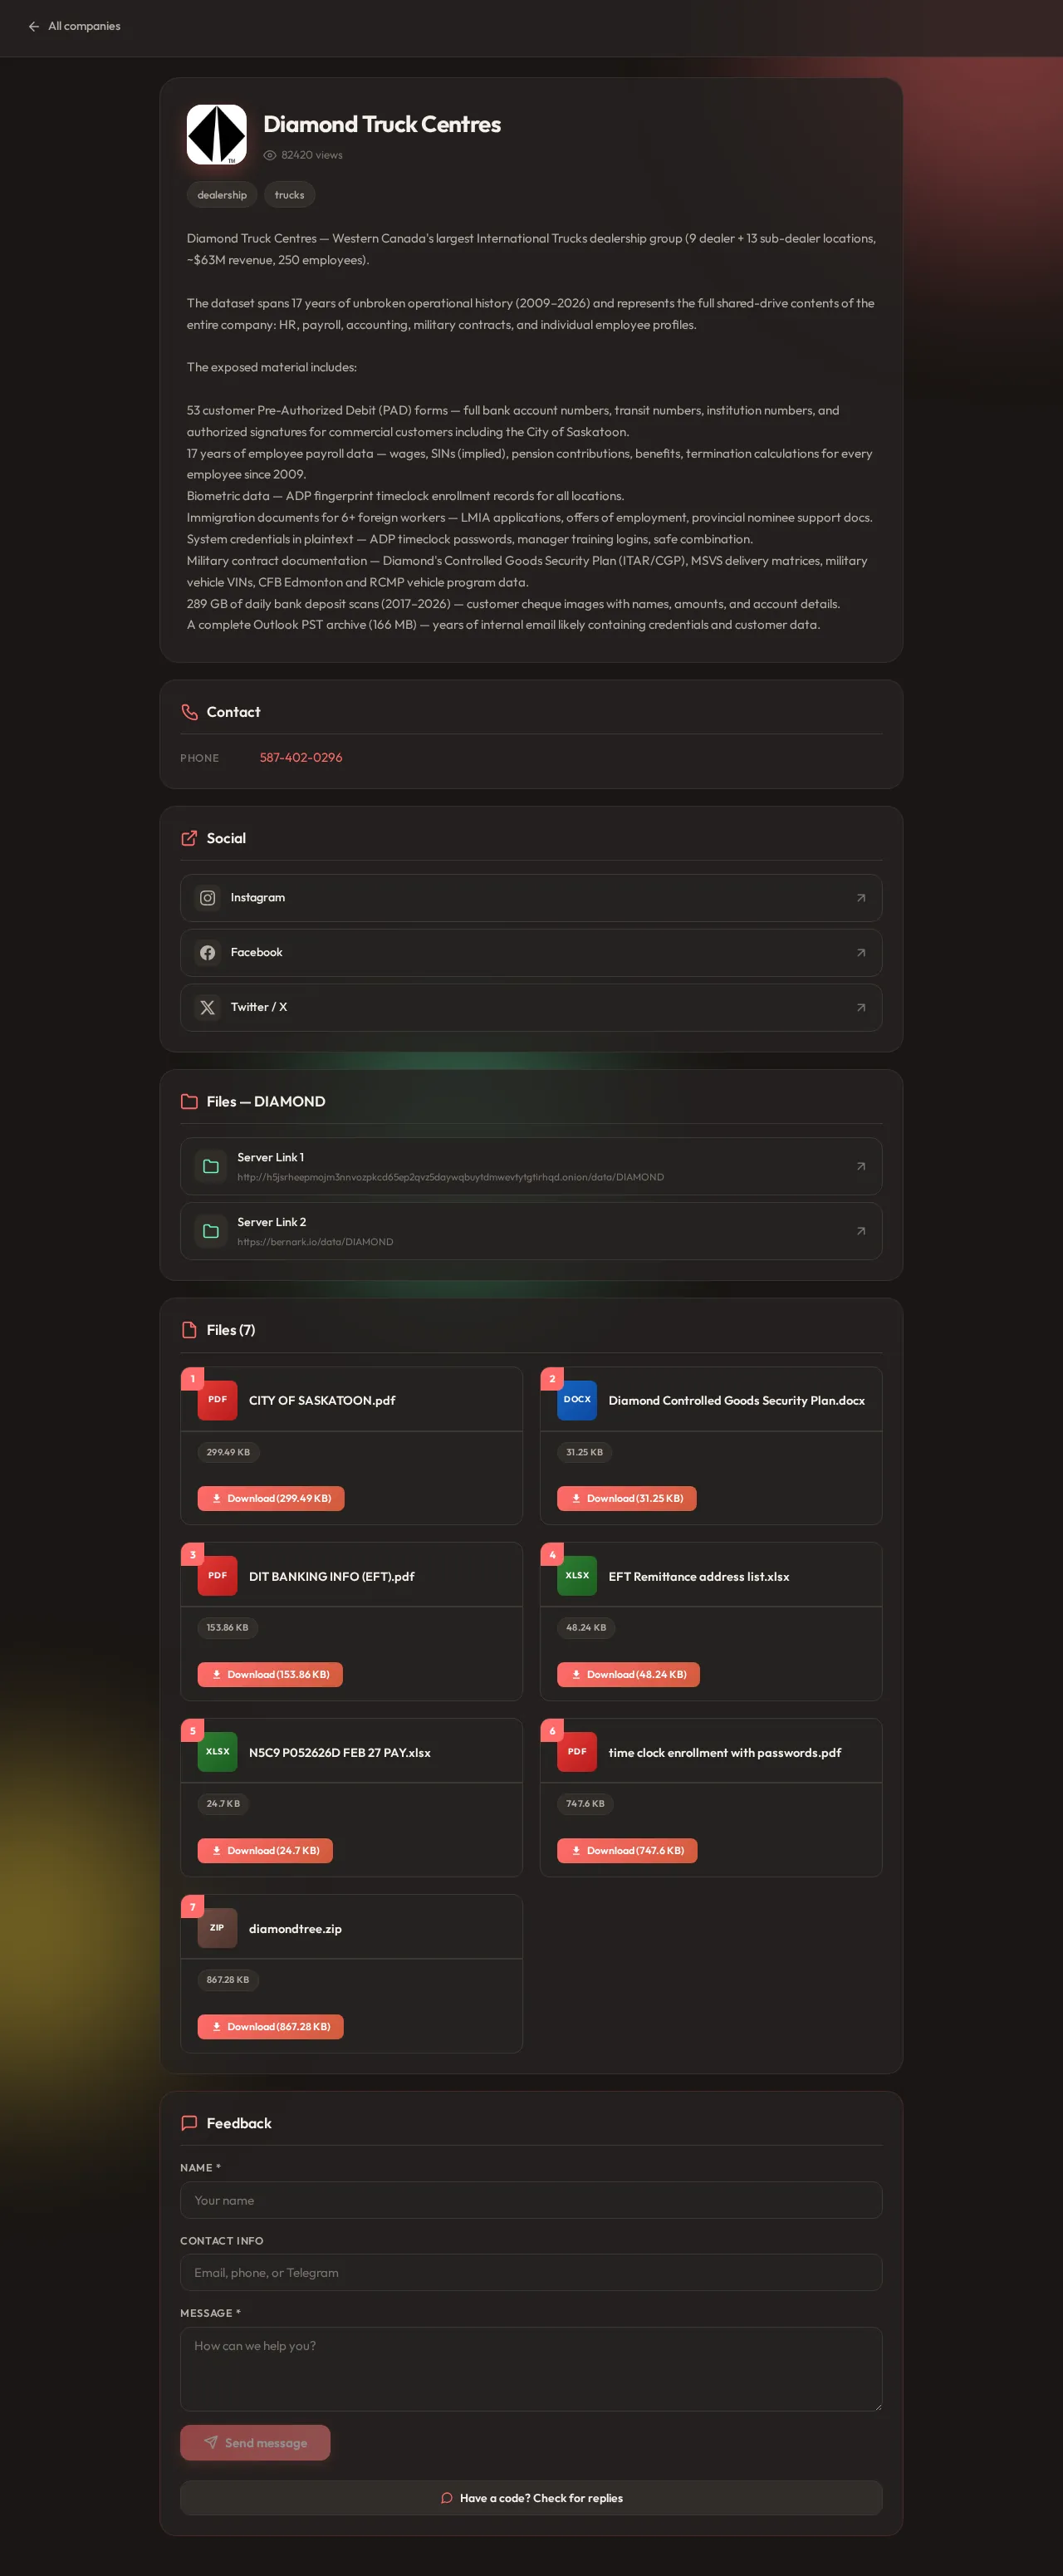
[dealership, trucks] *** — Western Canada's largest International Trucks dealership group (9 dealer + 13 sub-dealer locations, ~$63M revenue, 250 employees). The dataset spans 17 years of unbroken operational history (2009–2026) and represents the full shared-drive contents of the entire company: HR, payroll, accounting, military contracts, and individual employee profiles. The exposed material includes: 53 customer Pre-Authorized Debit (PAD) forms — full bank account numbers, transit numbers, institution numbers, and authorized signatures for commercial customers including the City of Saskatoon. 17 years of employee payroll data — wages, SINs (implied), pension contributions, benefits, termination calculations for every employee since 2009. Biometric data — ADP fingerprint timeclock enrollment records for all locations. Immigration documents for 6+ foreign workers — LMIA applications, offers of employment, provincial nominee support docs. System credentials in plaintext — ADP timeclock passwords, manager training logins, safe combination. Military contract documentation — Diamond's Controlled Goods Security Plan (ITAR/CGP), MSVS delivery matrices, military vehicle VINs, CFB Edmonton and RCMP vehicle program data. 289 GB of daily bank deposit scans (2017–2026) — customer cheque images with names, amounts, and account details. A complete Outlook PST archive (166 MB) — years of internal email likely containing credentials and customer data.
Leak Screenshots
1 CAPTUREDCaptured directly from the operator's leak site by our collector, last checked 2026-09-01. Verdict evidence: [H2] Download (299.49 KB)
Capture history — 5 day(s) tracked. Content is locked.