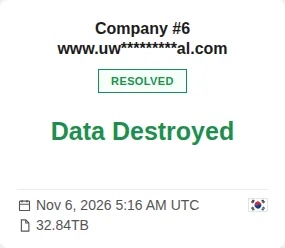
This record tracks a ransomware attack claimed by the
OBSOFT group against
Company #6. It collects the publicly disclosed attack details — sector, location and
timeline — as published on the operator's leak site and indexed by Dark Eye.
Window Zero
EXPOSURE GAP
Window Zero is the time the breach stayed in the open before
anyone said so — the gap between when the attack was first discovered
on the operator's leak site (t1) and when it was publicly disclosed (t2).
The wider this window, the longer victims, staff and customers were exposed with no warning.
16days open
t1 · Published
t2 · Pending
Indexed by Dark Eye
November 06, 2026
Leak Status
pending
checked 2026-11-22
Disclosed / Notified
Not disclosed yet
Attack Summary
UW Medical Center is a major academic health system based in Seattle, Washington, operating multiple hospitals and clinics. It provides a wide range of medical services, including emergency care, surgery, pediatrics, and specialized treatments. The health system is affiliated with the University of Washington School of Medicine and is known for its research and educational programs. UW Medical Center was listed as a ransomware victim by the threat actor OBSOFT, indicating a potential cyber incident affecting its operations or data.
Leak Screenshots
1 CAPTURED
Captured directly from the operator's leak site by our collector, last checked 2026-11-22. Verdict evidence: [I1] Redacted victim card identified; no verifiable evidence of publication
Showing the latest capture only
Unlock the daily capture history — up to 45 days of evidence.
Dark Web Exposure
Findings for uw*********al.com
— indexed by HaveIBeenRansom.
0
found in Infostealer logs
373+
found in Traditional breaches
75+
found in Ransomware leaks
VerificationsIO_BF.7z.011
Kedr | Forum · breach
••• emails
Arandell Corp
medusa · ransomware
••• emails
McKesson Corporation
shinyhunters · ransomware
••• emails
shouldve_paid_the_ransom_PITNEYBOWES-SHINYHUNTERS.7z
Database World ROC · breach
••• emails
Pitney Bowes Inc. (pb.com)
shinyhunters · ransomware
••• emails
B F R e p o V 3 F i l e s · breach
••• emails
+ 17 more leak sources locked
Leak volumes are locked
Sign in to reveal how many records each source exposed and the remaining 20 sources.
Legal Disclaimer:
This ransomware victim record reflects information published on the operator's leak site.
Dark Eye only records what the operators themselves publish in the
open. We take screenshots of their public pages and keep the proof
material they post there, so that a listing can be verified and its status
tracked over time. We do not purchase data, we do not solicit or encourage
its publication, we do not access any private system, and we do not alter
anything we record. Nothing is offered for download here, and detailed
content is not published on this page or anywhere else on the public site:
access to it is restricted to vetted customers under contract, for
incident response, due diligence and cyber-resilience work.
Dark Eye is not affiliated with, and does not act on behalf of, the
operators who publish this material. If you represent an organisation or
individual named here and want a record reviewed or removed, contact us
and we will act on it.