Hurley
playThis record tracks a ransomware attack claimed by the play group against Hurley. It collects the publicly disclosed attack details — sector, location and timeline — as published on the operator's leak site and indexed by Dark Eye.
Window Zero
EXPOSURE GAPWindow Zero is the time the breach stayed in the open before anyone said so — the gap between when the attack was first discovered on the operator's leak site (t1) and when it was publicly disclosed (t2). The wider this window, the longer victims, staff and customers were exposed with no warning.
Attack Summary
www.hurleyco.net is a United States-based company operating within the Services sector, providing commercial and professional offerings relevant to its industry. The entity is cataloged in this threat-intelligence index under the listing type ransomware victim, with the associated threat actor or source identified as 'play'. This designation reflects the cybersecurity context in which the organization was documented, emphasizing the need for defenders to monitor related activity and understand potential impacts on Services-sector entities. The description remains factual and neutral, focusing solely on the indexed classification without elaborating on unverified incident details. It was listed as a ransomware victim associated with play.
Leak Screenshots
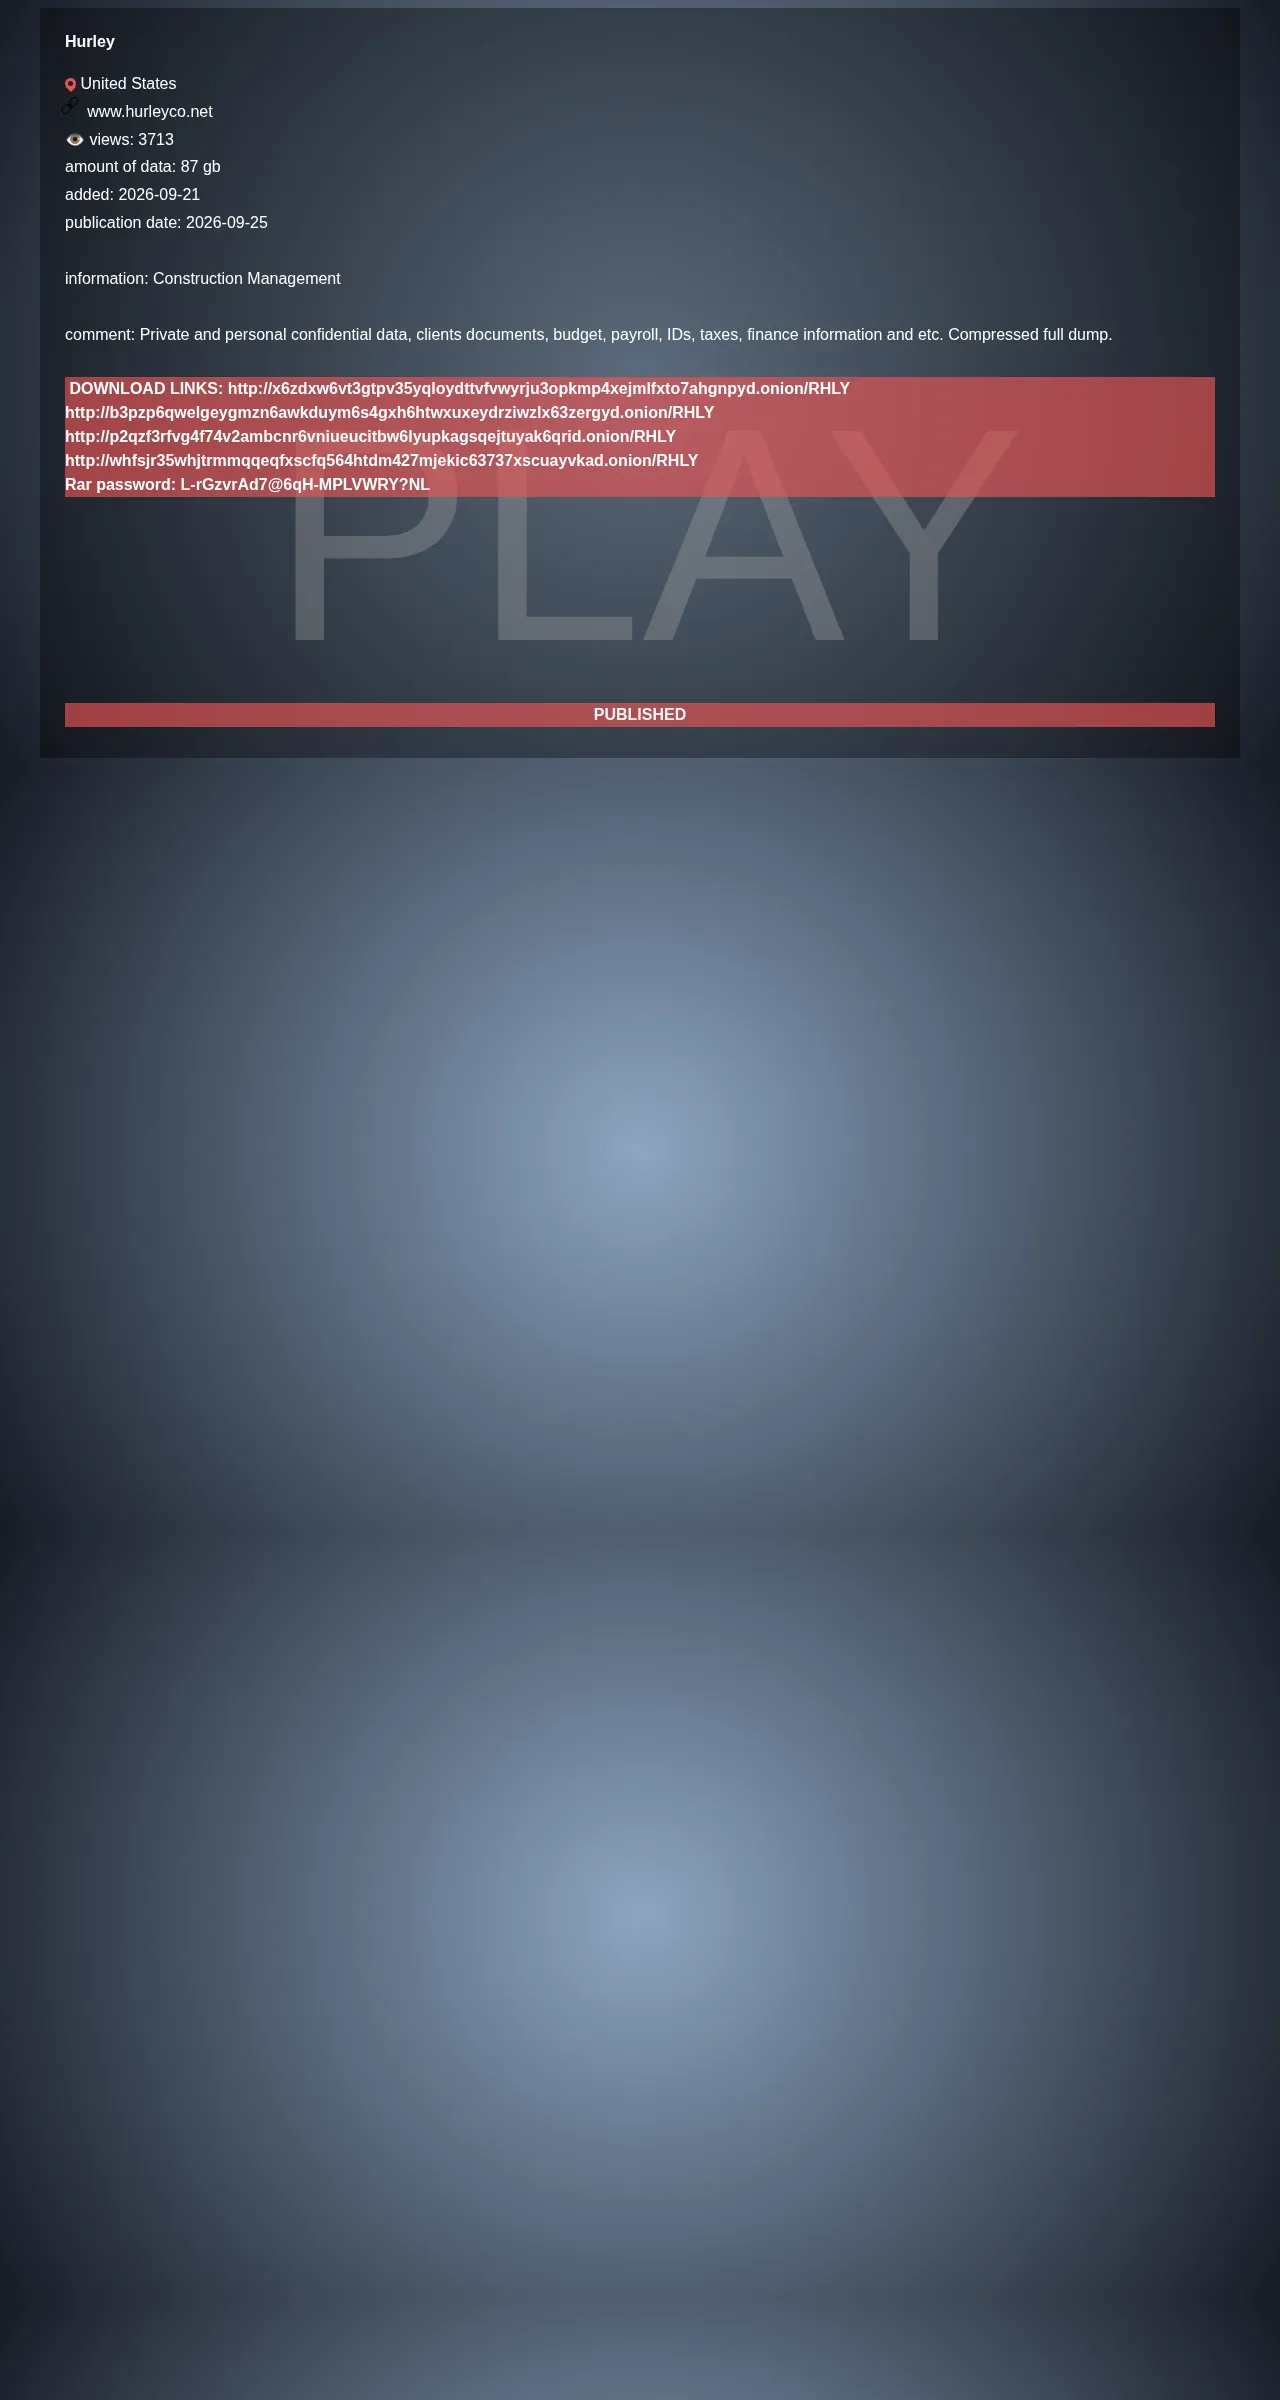
1 CAPTUREDCaptured directly from the operator's leak site by our collector, last checked 2026-10-01. Verdict evidence: [H2] DOWNLOAD LINKS: http://x6zdxw6vt3gtpv35yqloydttvfvwyrju3opkmp4xejmlfxto7ahgnpyd.onion/RHLY
Capture history — 6 day(s) tracked. Content is locked.