Nintendo
ShadowByt3$This record tracks a ransomware attack claimed by the ShadowByt3$ group against Nintendo. It collects the publicly disclosed attack details — sector, location and timeline — as published on the operator's leak site and indexed by Dark Eye.
Window Zero
EXPOSURE GAPWindow Zero is the time the breach stayed in the open before anyone said so — the gap between when the attack was first discovered on the operator's leak site (t1) and when it was publicly disclosed (t2). The wider this window, the longer victims, staff and customers were exposed with no warning.
Attack Summary
Nintendo Co., Ltd. is a Japanese corporation headquartered in Kyoto specializing in video game development, software, hardware, entertainment services, and digital platform offerings across global markets. Operating within the manufacturing and engineering sector, Nintendo designs consoles, game engines, publishing systems, and related consumer electronics with a long-established presence in Japan and worldwide markets. This entity has been cataloged in the threat-intelligence index as a ransomware victim associated with the threat actor ShadowByt3$, reflecting its inclusion in cybersecurity intelligence records for this incident type. The description remains neutral regarding confirmed technical details, data impacts, or operational consequences, adhering strictly to disclosed classification information.
Leak Screenshots
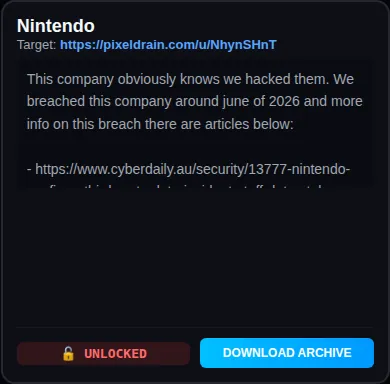
1 CAPTUREDCaptured directly from the operator's leak site by our collector, last checked 2026-10-30. Verdict evidence: [M1] This company obviously knows we hacked them. We breached this company around june of 2026 and more info on this breach there are articles below:
Capture history — 3 day(s) tracked. Content is locked.